GDPR-compliant analytics that doesn't need a consent banner
Google Analytics needs explicit consent, and banner-dismissal rates kill your attribution data. Mixpanel and Amplitude route data through US servers, which Schrems II made a legal mess. MakinForU is cookieless, EU-hosted, and self-hostable for full data sovereignty. No banner. No DPA hell. No US transfer risk.
- EU-hosted
- Cookieless by default
- No consent banner required
- Self-host for full sovereignty
Why most analytics tools are a GDPR liability
The analytics stack most teams default to creates GDPR compliance work that scales worse than the tools themselves.
GA4 requires explicit consent — which most users decline
Consent banner dismissal and rejection rates routinely run 30–60%. That means up to half your traffic is invisible to GA4 by design, your conversion attribution is broken, and you're paying for a tool you can't use on the data that matters most.
US-based tools mean Schrems II risk
Mixpanel, Amplitude, PostHog Cloud, and Heap all process EU data on US infrastructure. The EU-US Data Privacy Framework patched the legal hole but EU DPAs continue to scrutinize US transfers. One adequacy challenge and your processor list is suddenly a compliance problem.
DPAs and BAAs are operational overhead — most teams skip them
Every SaaS analytics tool you use as a processor needs a signed DPA. Healthcare-adjacent teams need BAAs. Most engineering teams don't track which tools have signed paperwork, which means most production analytics setups quietly fail their first GDPR audit.
Cookie consent rejection = no data
Even when banners show, modern users dismiss them fast. The data you're collecting is the data from users who didn't notice the banner — not your real audience. Cookieless analytics is the structural fix; bolting consent on top of GA4 is not.
How MakinForU makes GDPR analytics painless
Architecture-level decisions — not consent-banner workarounds — that put MakinForU inside GDPR's legitimate-interest basis from the start.
Cookieless tracking by default
MakinForU identifies sessions via a privacy-preserving daily-rotating hash of IP + user agent — no personal data persists beyond 24 hours. No cookies set, no PECR (EU cookie directive) consent required, no banner needed for product analytics.
EU-hosted cloud option
MakinForU collects no personal data to transfer: IP addresses are used to derive a country and a daily-rotating hash, then discarded. If your policy still requires EU residency, self-host MakinForU inside the EU and no third party is involved at all.
Self-host for total data sovereignty
Run MakinForU on your own infrastructure (Docker Compose: ClickHouse + Postgres + Redis, one-command setup). Your servers, your data, your jurisdiction. No third-party processor, no DPA to sign with anyone.
IP anonymization built-in
Raw IP addresses are never stored — they're hashed for the session identifier and discarded. Geo data is derived from the hash, not the IP. No configuration required.
Open-source codebase you can audit
MIT-licensed. Show your DPO exactly which fields are collected, how they're hashed, and where they're stored. Competing tools can only ask you to take their word for it.
Data subject request tooling
Export or delete all data for a specific user via the API. Build automated GDPR Article 15 (access) and Article 17 (erasure) flows in minutes, not days.
No third-country data transfers
Self-hosting means you are the only processor — no Standard Contractual Clauses, no transfer impact assessments, no Chapter V exposure. MakinForU Cloud is hosted in India, so EU customers using the cloud rely on Standard Contractual Clauses; the DPA covers this.
Audit-friendly architecture
Every data flow is documented in open code. Hand the architecture diagram to your auditor; no proprietary 'trust us' to defend.
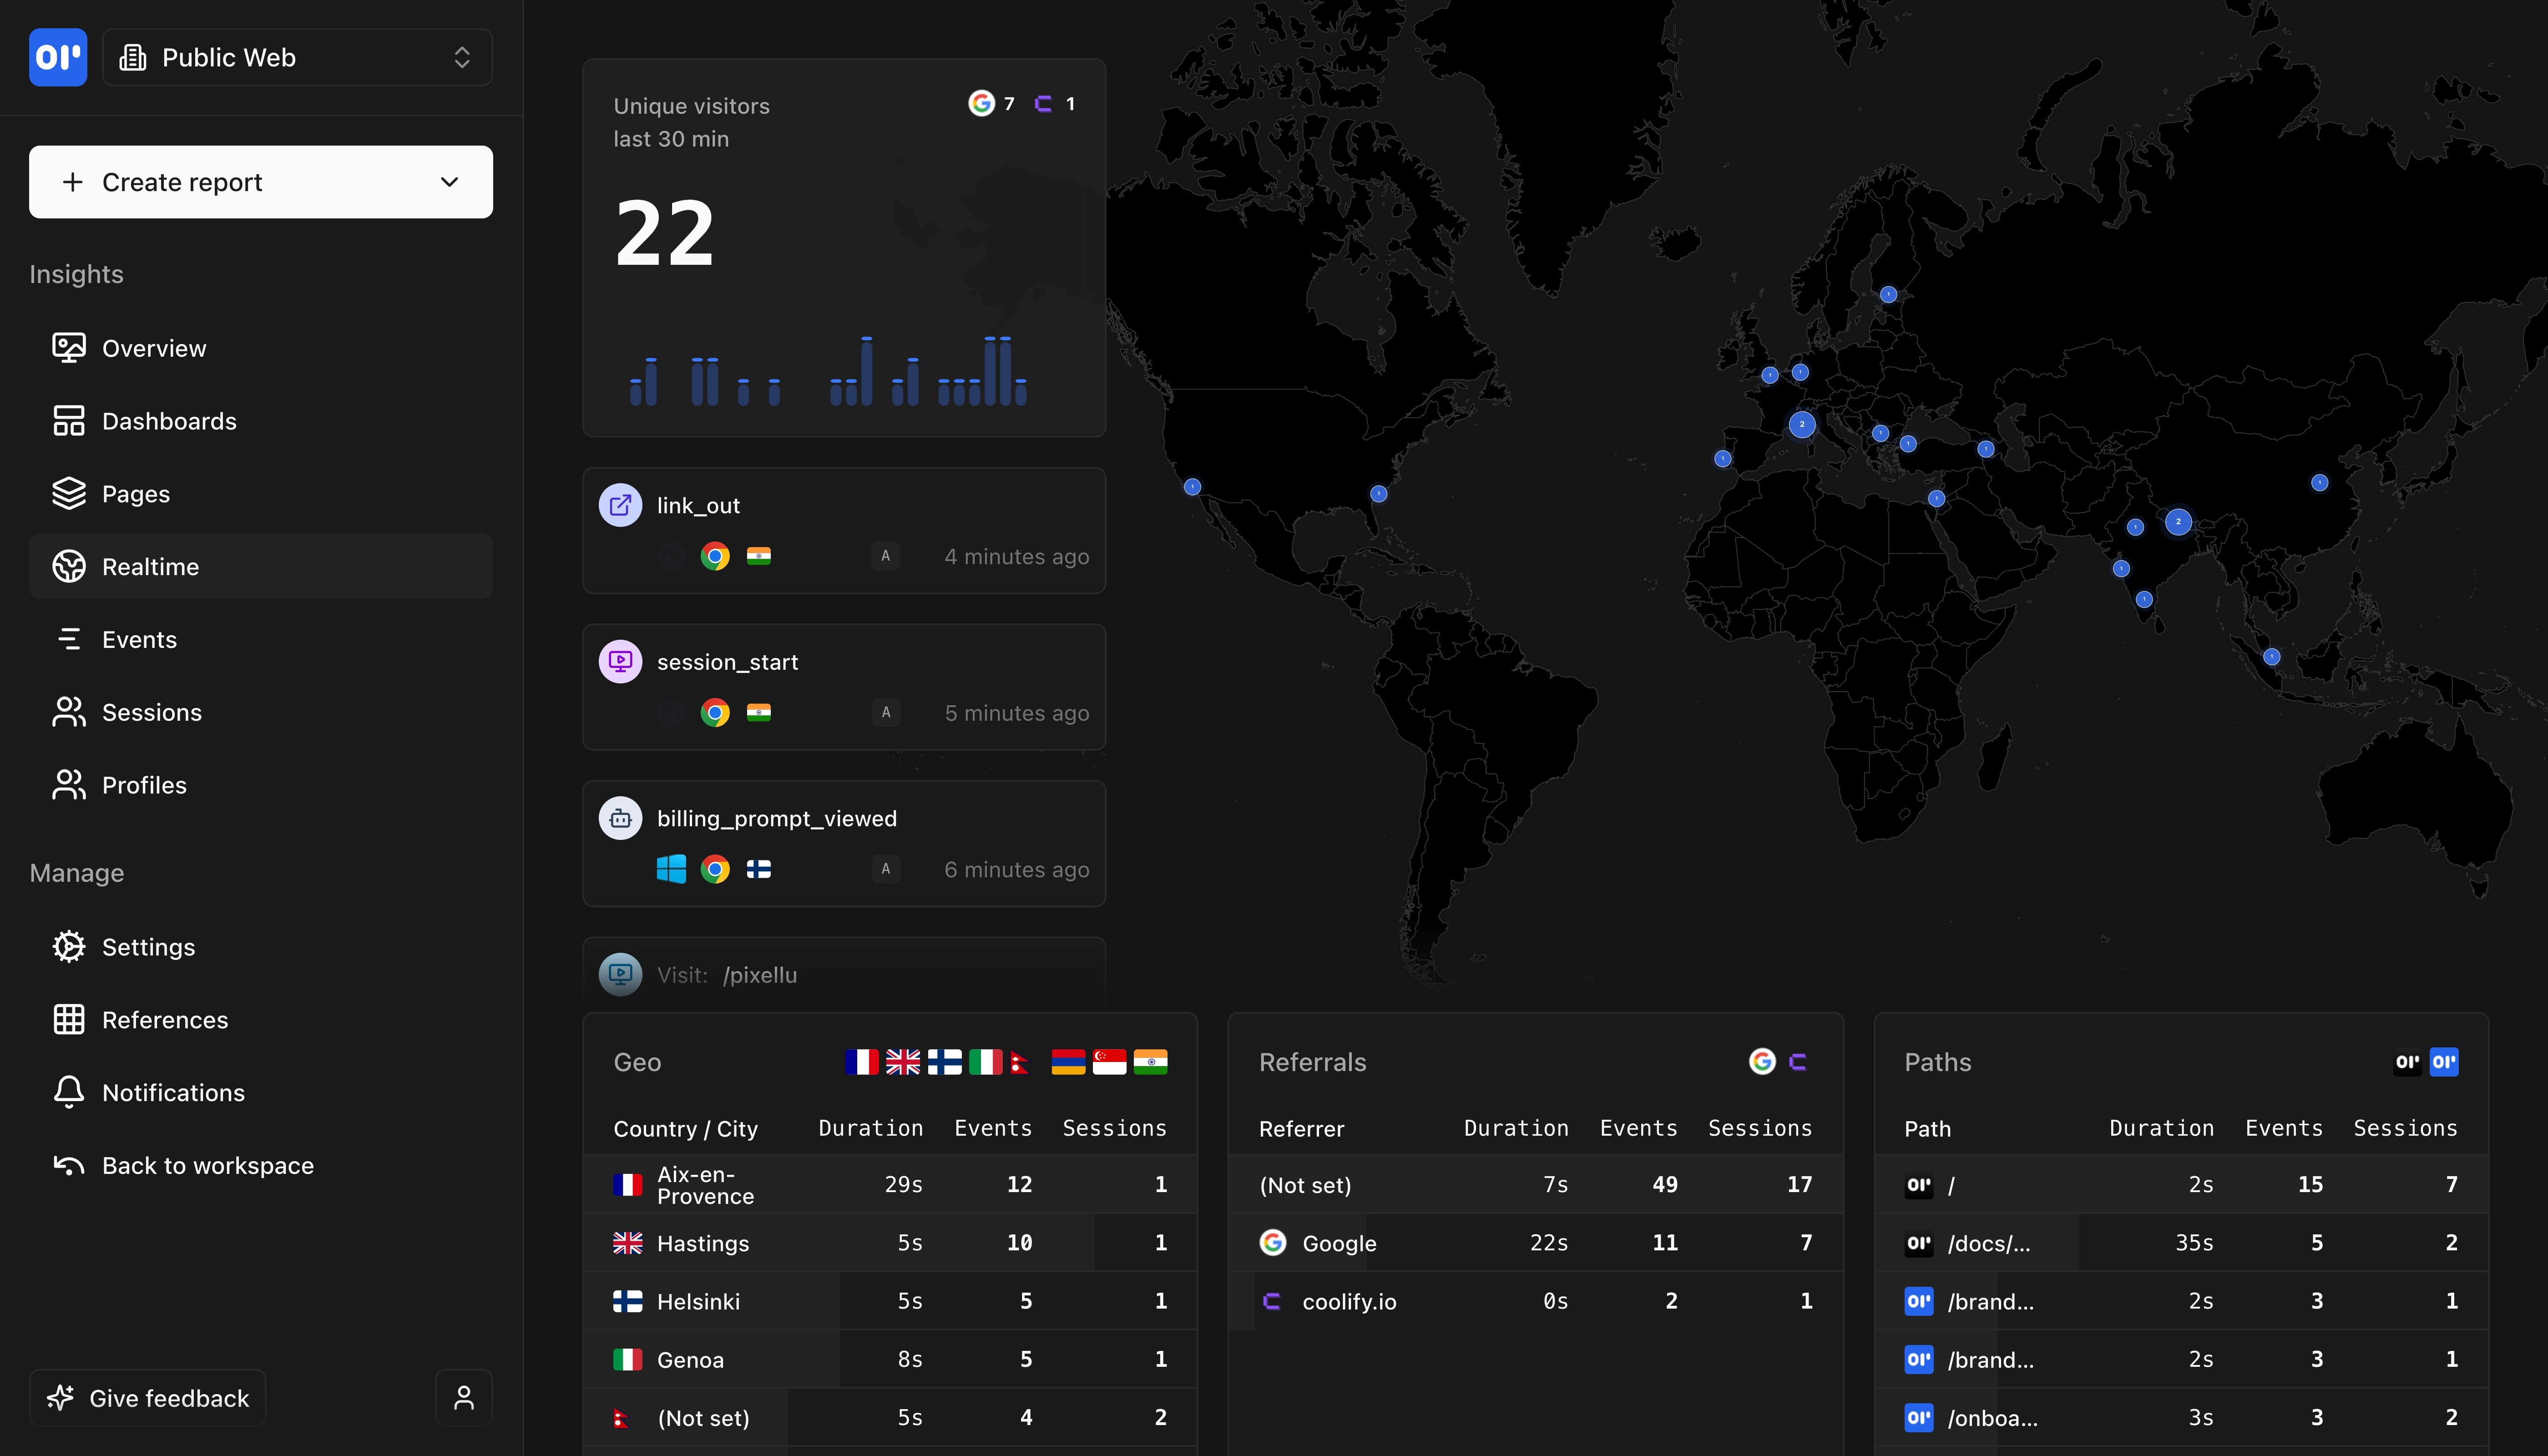
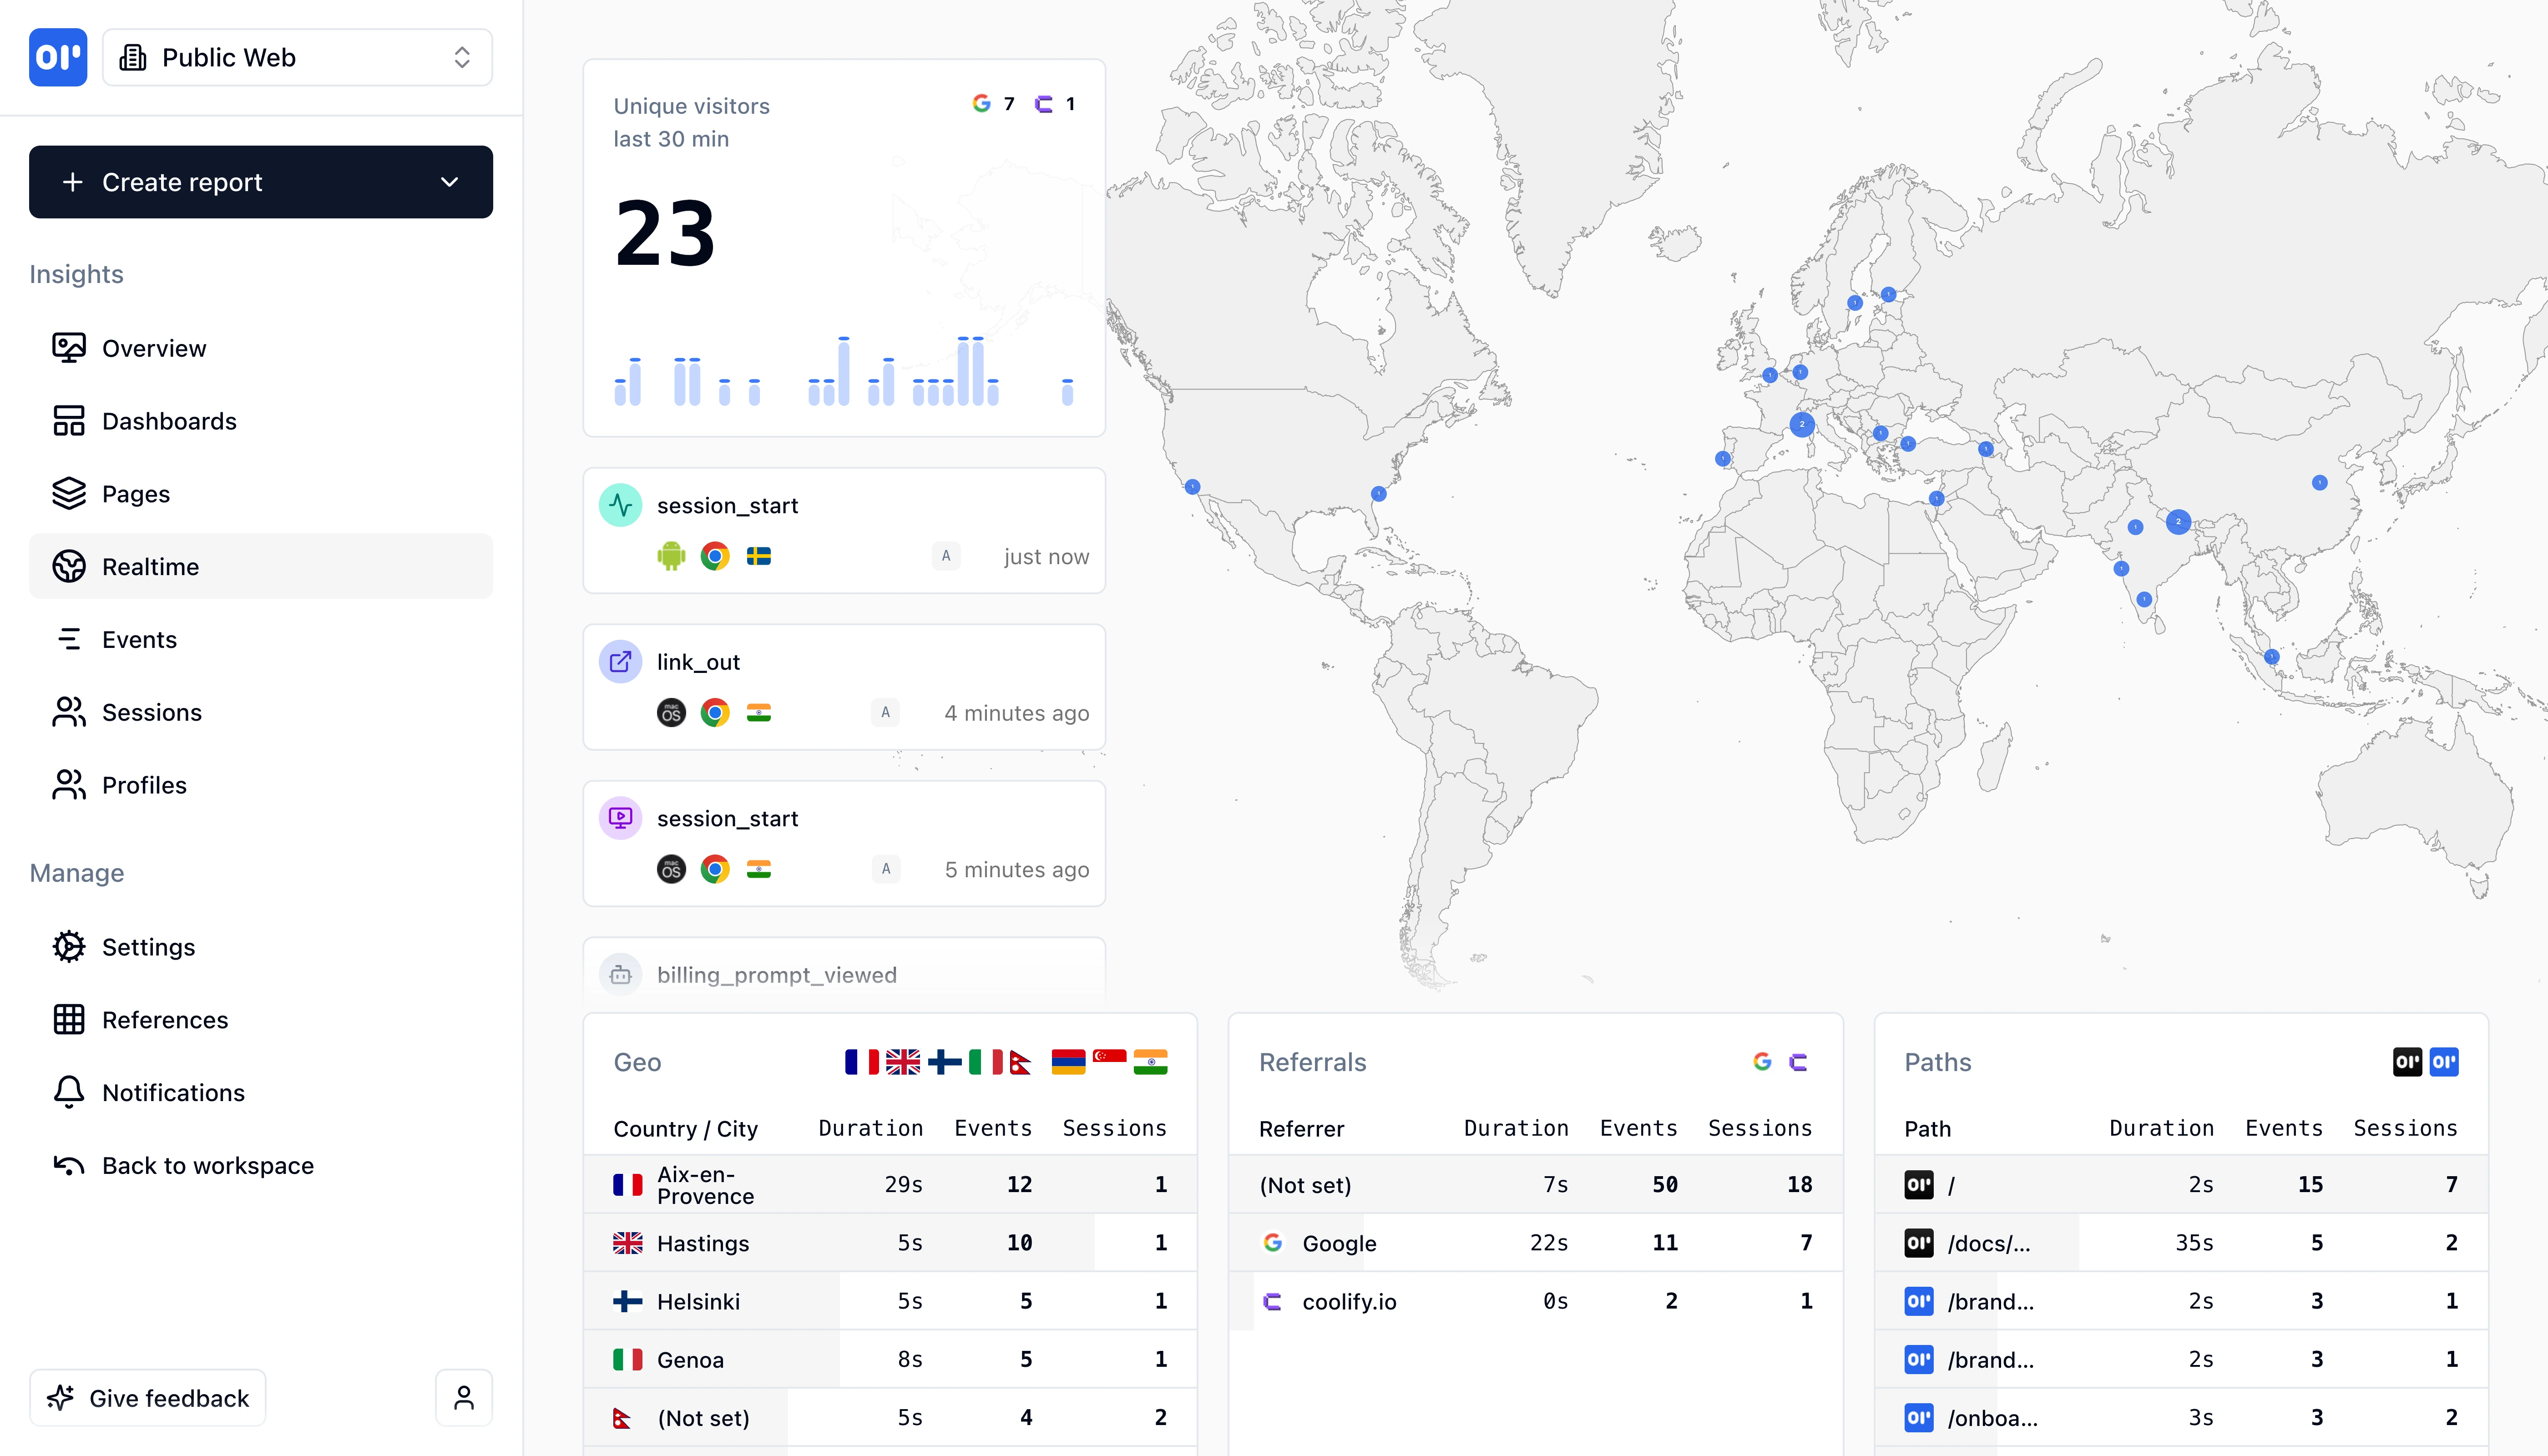
Why privacy-conscious teams pick MakinForU
The compliance benefits show up in your data quality, your legal review cycle, and your audit response time.
Get the real attribution picture
Cookieless tracking captures all your traffic, not just consenting users. Conversion attribution, funnel analysis, and retention metrics finally reflect reality.
No DPA paperwork burden
Self-hosted MakinForU is not a third-party processor — there's nothing to sign. Cloud users get one DPA from MakinForU instead of a stack from separate vendors.
Pass GDPR audits without scrambling
Architecture-level privacy means the auditor's questions ('What's the lawful basis? Where's the data? Who's the processor?') have one-line answers.
Compliance scales with the company
As you expand into healthcare, financial services, or EU public-sector contracts, the architecture already meets the higher bar. No re-platforming for stricter audits.
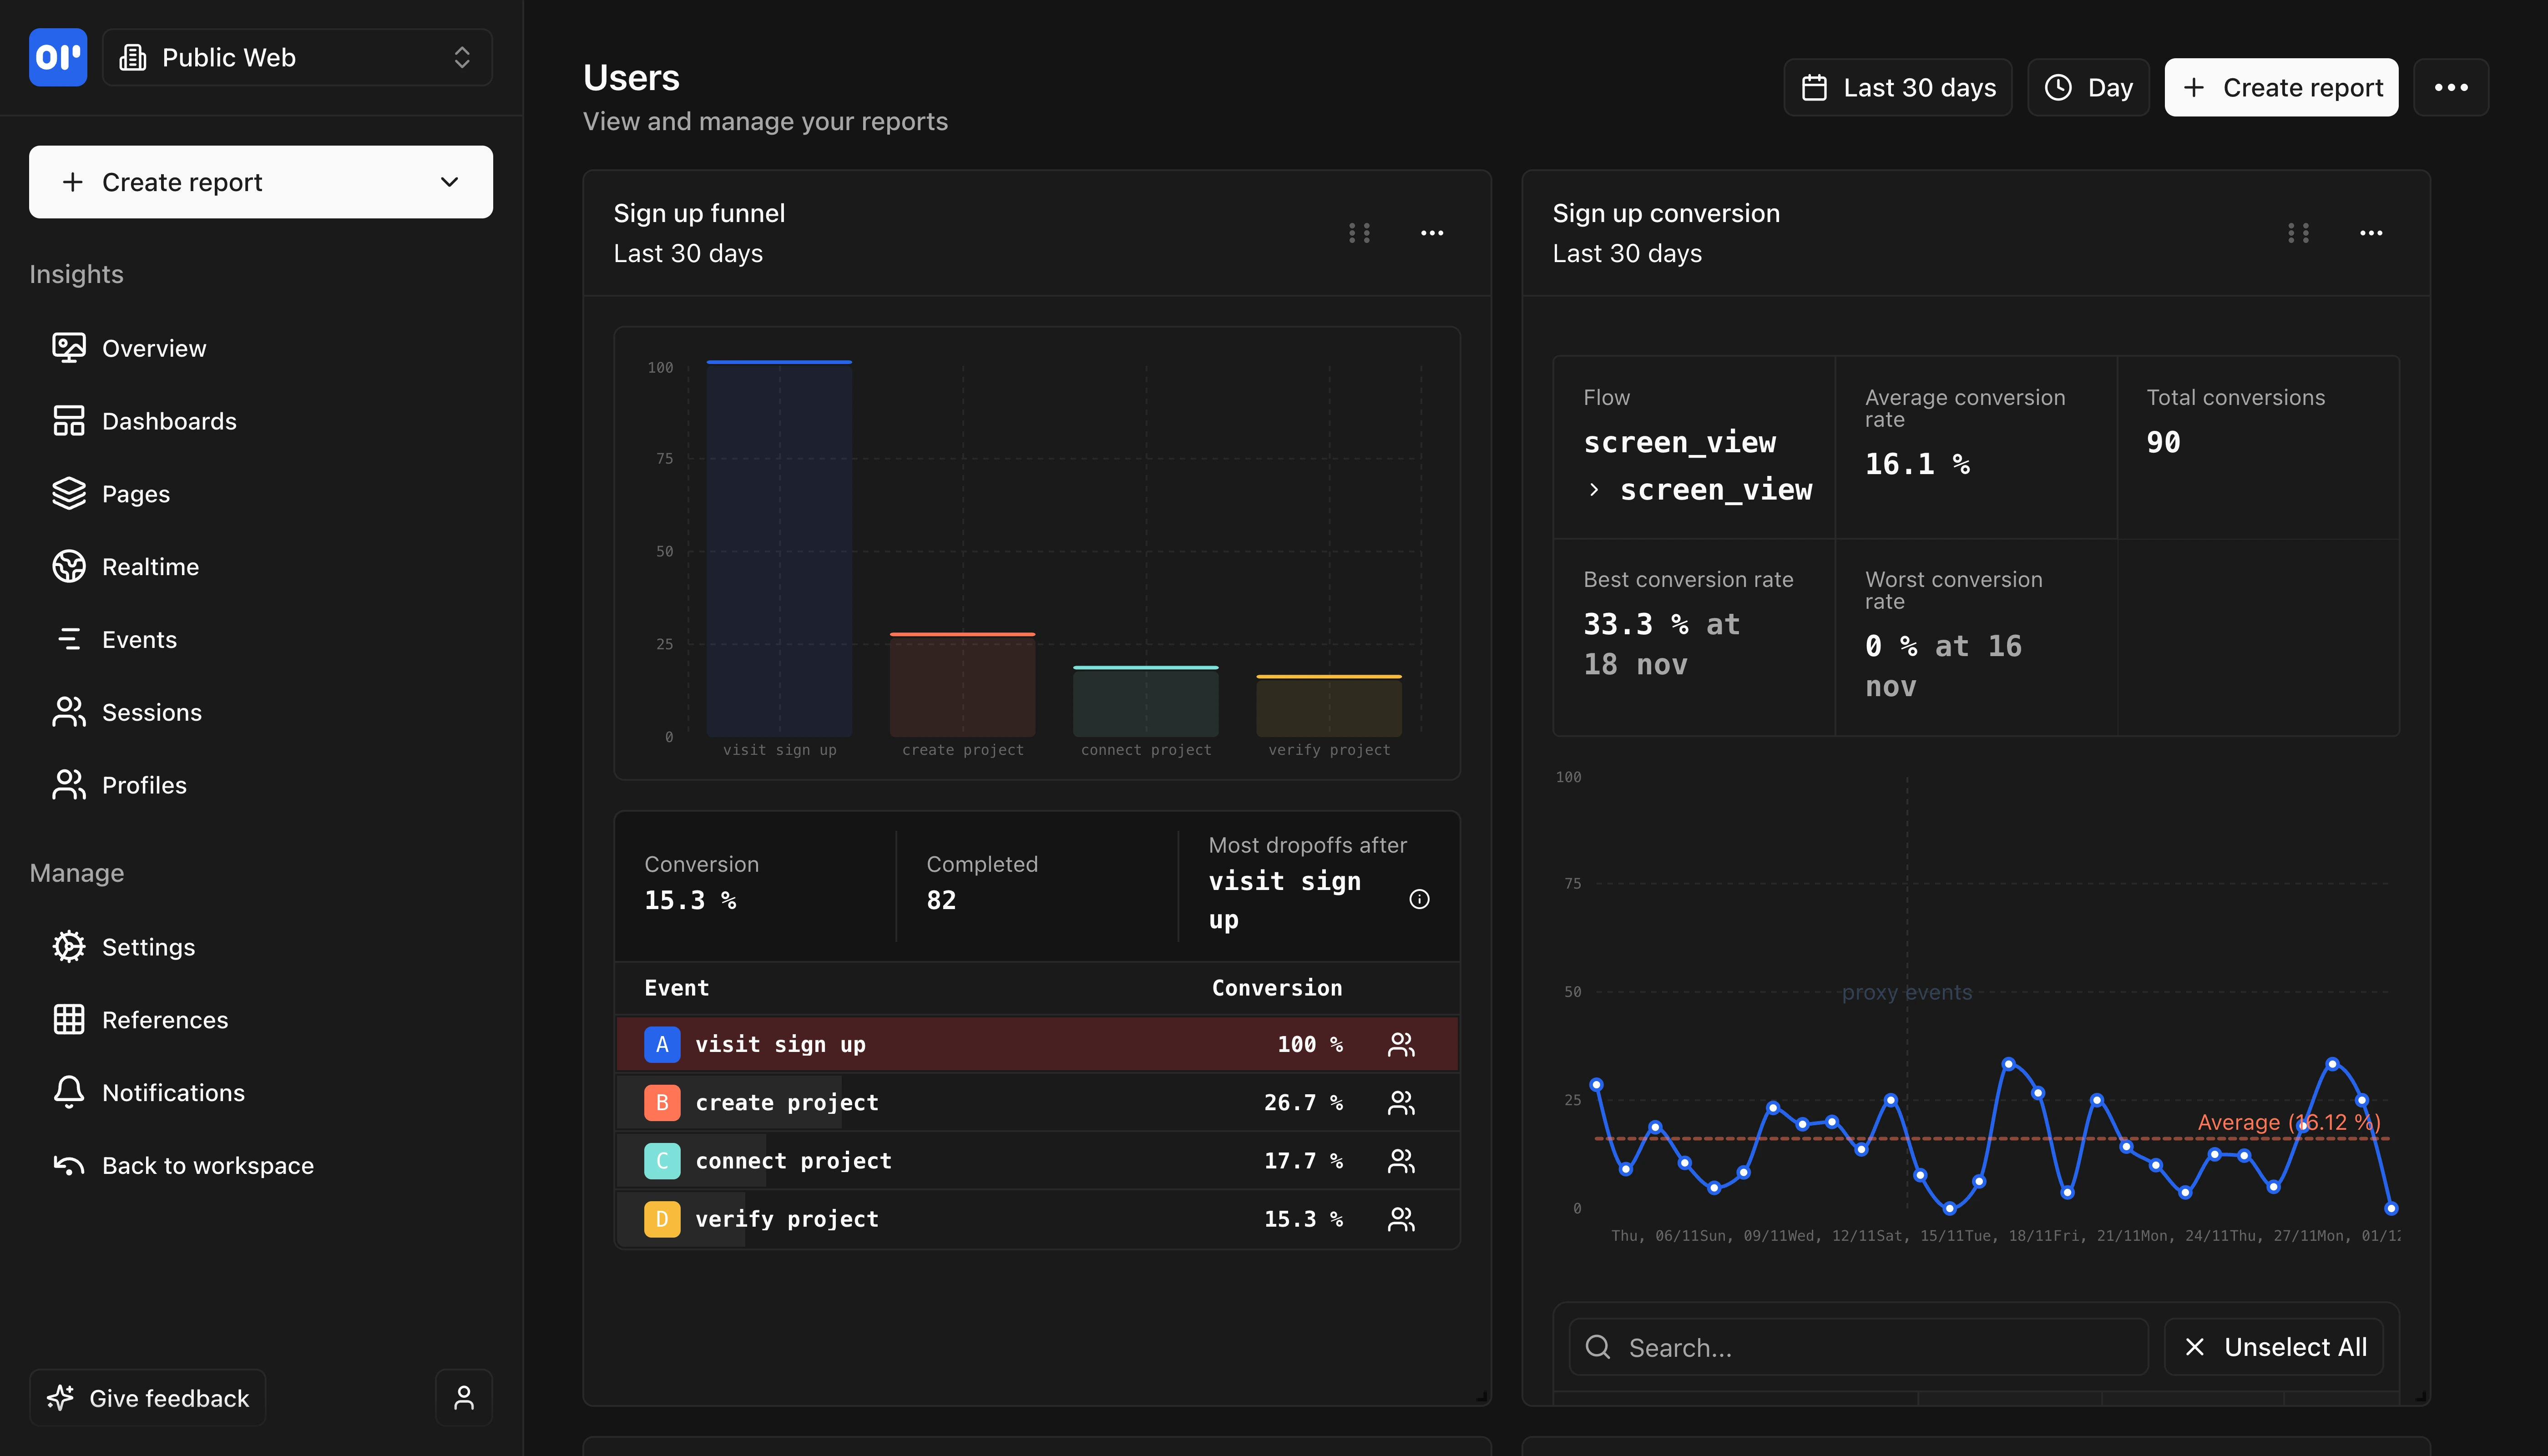
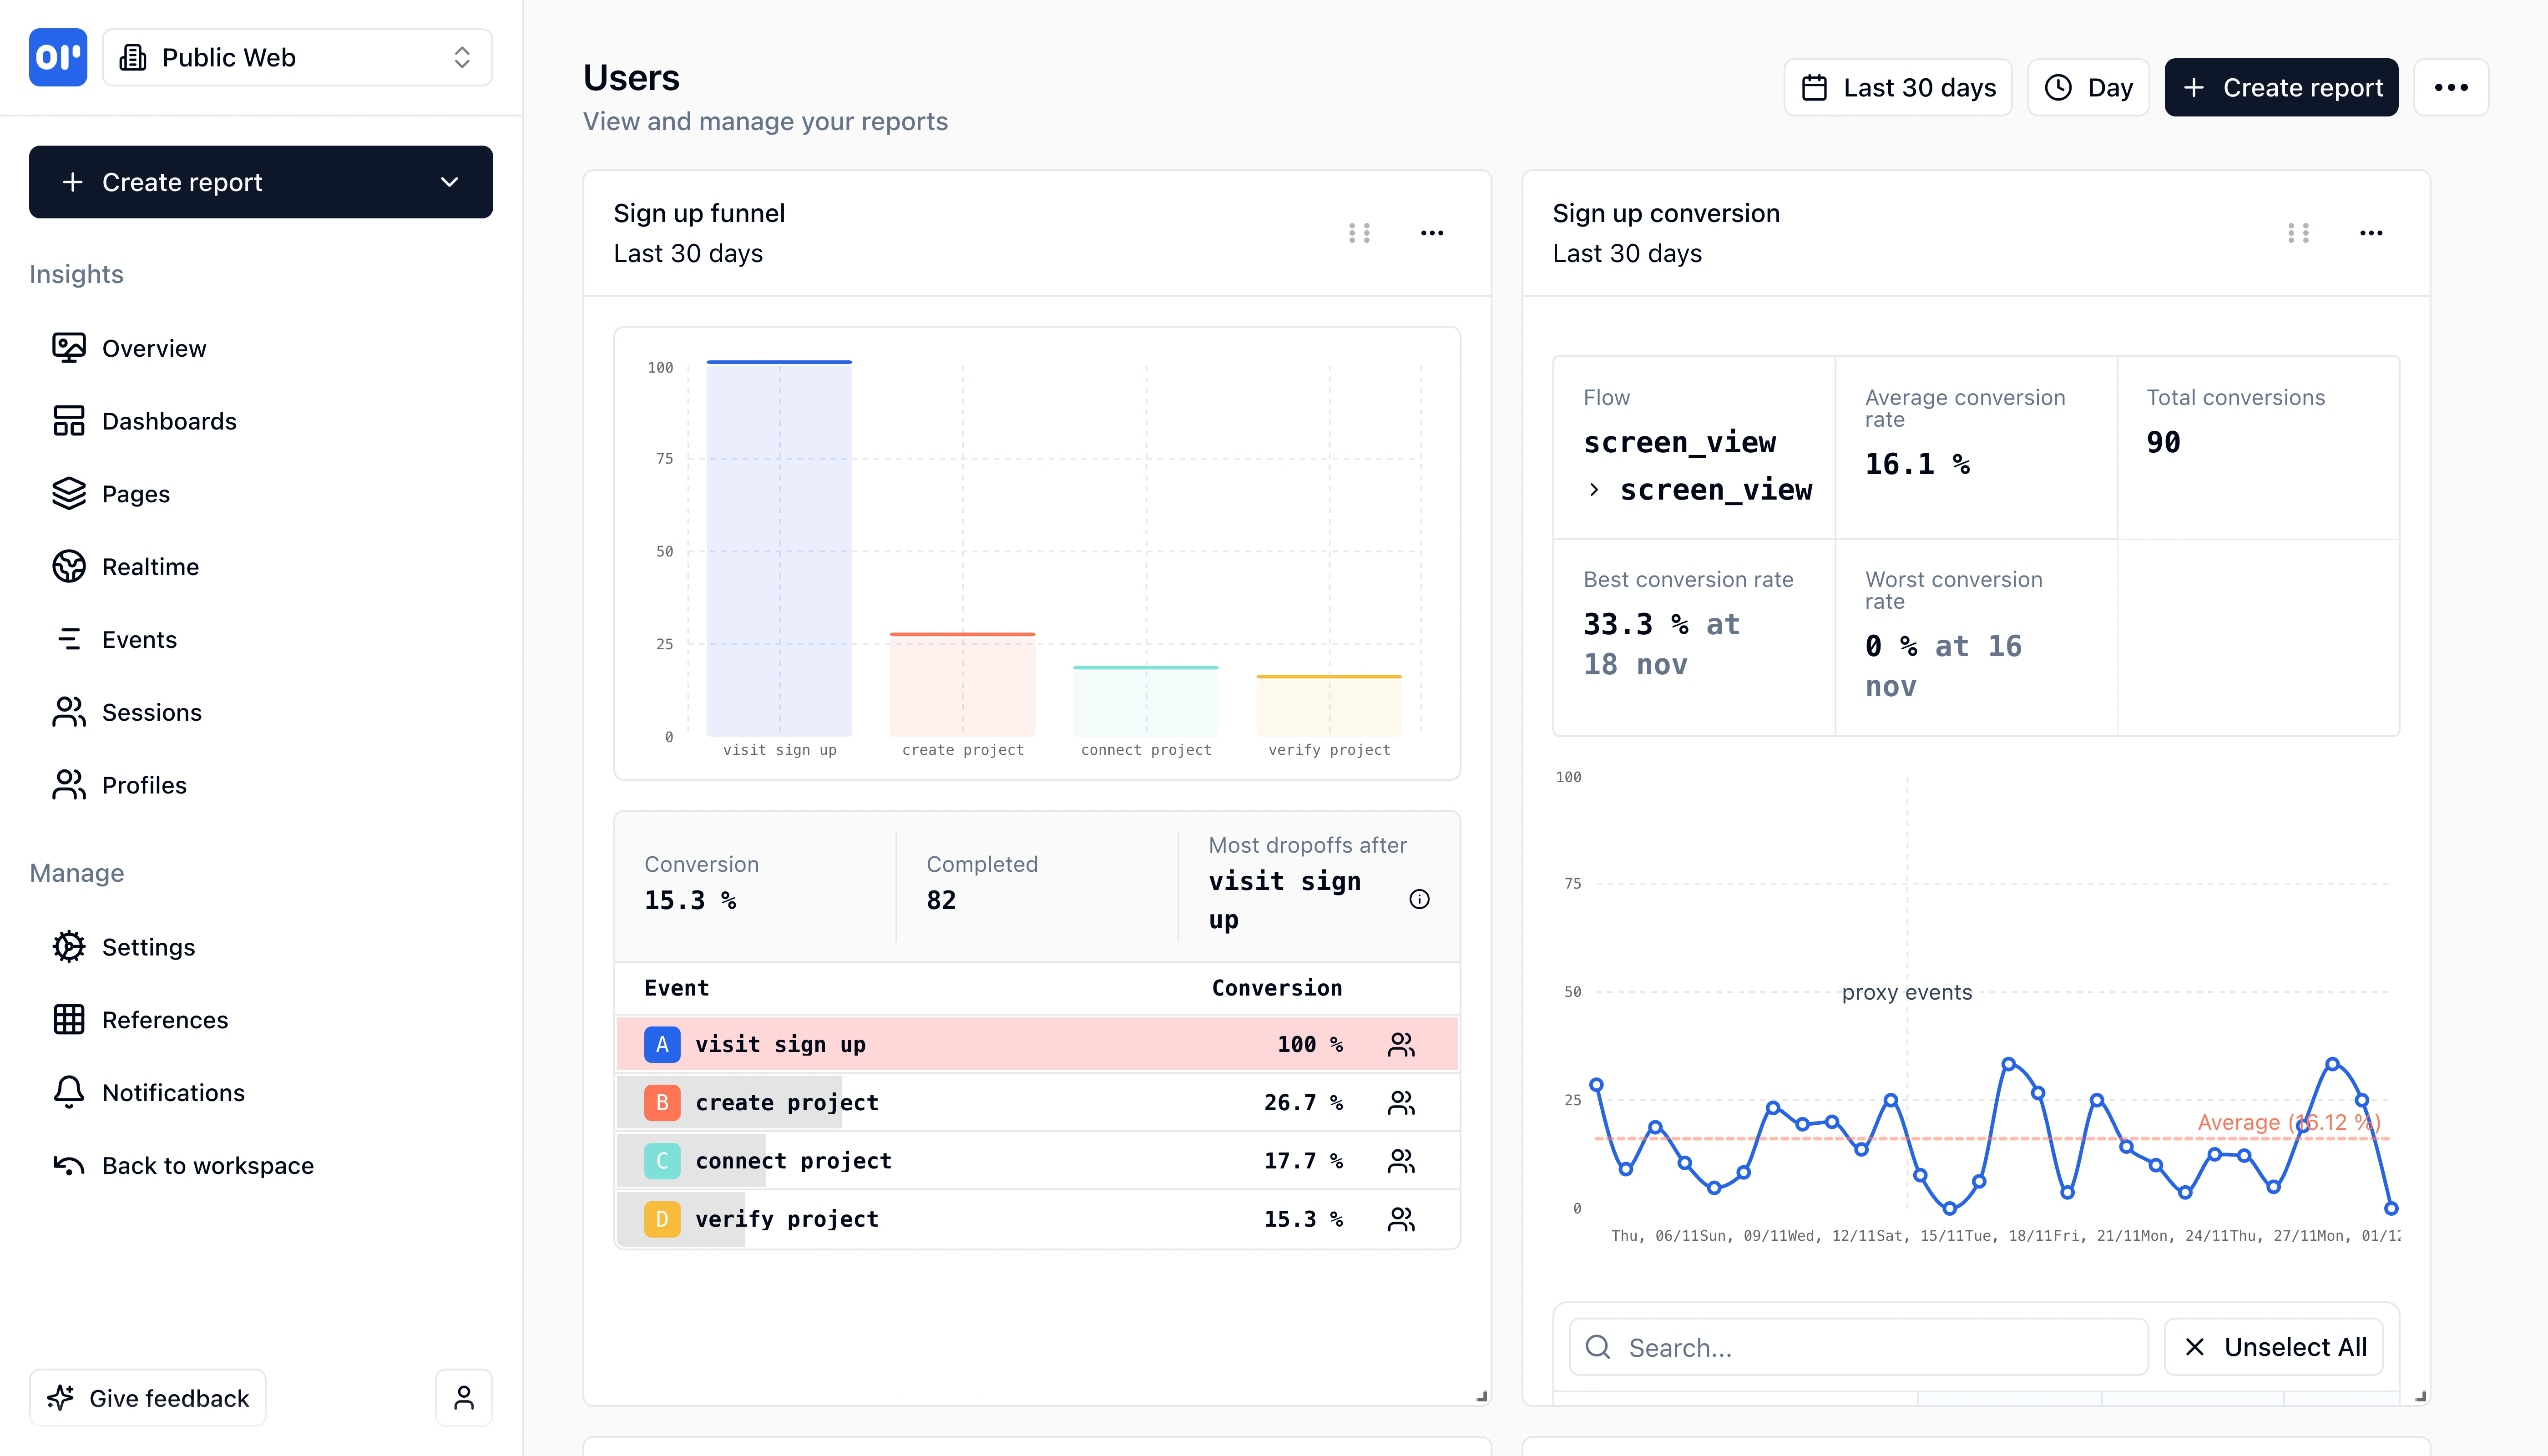
Frequently asked questions about GDPR-compliant analytics
Common questions from privacy engineers, DPOs, and founders evaluating MakinForU for EU compliance.
Related resources
Learn more about MakinForU and how it can help you.
Ready to get started?
Test MakinForU free for 30 days, you'll not be charged anything unless you upgrade to a paid plan.
Try MakinForU Free